FuzzingLabs created FuzzForge, an offensive security platform that helps product security teams and PSIRTs continuously validate the security and compliance of their embedded products through the orchestration of specialised AI agents.




THE PROBLEM
The attack surface is code you cannot open. Firmware, binaries and embedded systems run critical functions, and classic tools need the source to see anything.
The people who can test it are rare. A researcher who can reverse an embedded firmware is far rarer than a web pentester, and you will not close that gap by hiring.
The old playbook cannot keep up. Products ship continuously, and the gap between a disclosed flaw and its exploit keeps shrinking. A yearly audit ages the day it lands.
PRODUCT & TRAINING
PROOF
ABOUT
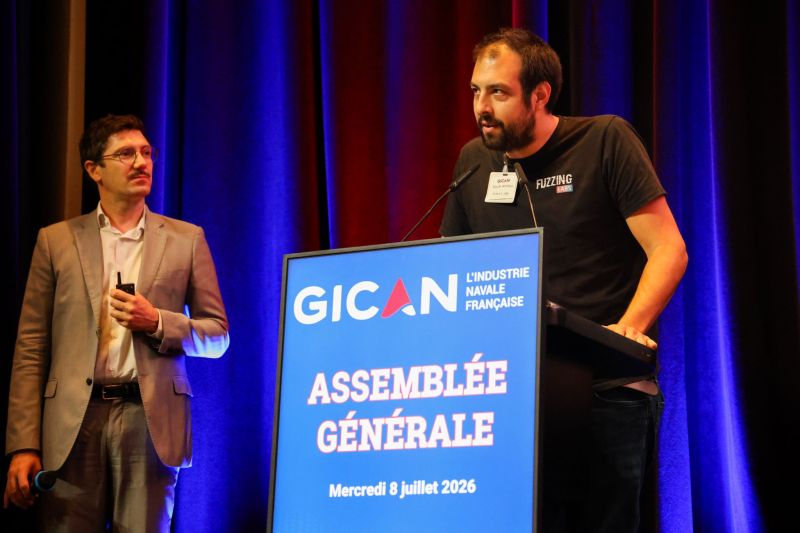
FuzzingLabs was founded in 2021 by Patrick Ventuzelo, a vulnerability researcher who spent more than ten years finding the flaws hidden in firmware and binaries. He built FuzzingLabs to turn that passion into a company, and to teach it.
Today, FuzzingLabs is a French team of researchers and engineers. They compete at Pwn2Own, present at Black Hat and OffensiveCon, and pour that same passion into FuzzForge, the platform at the heart of the company.
THE FLYWHEEL
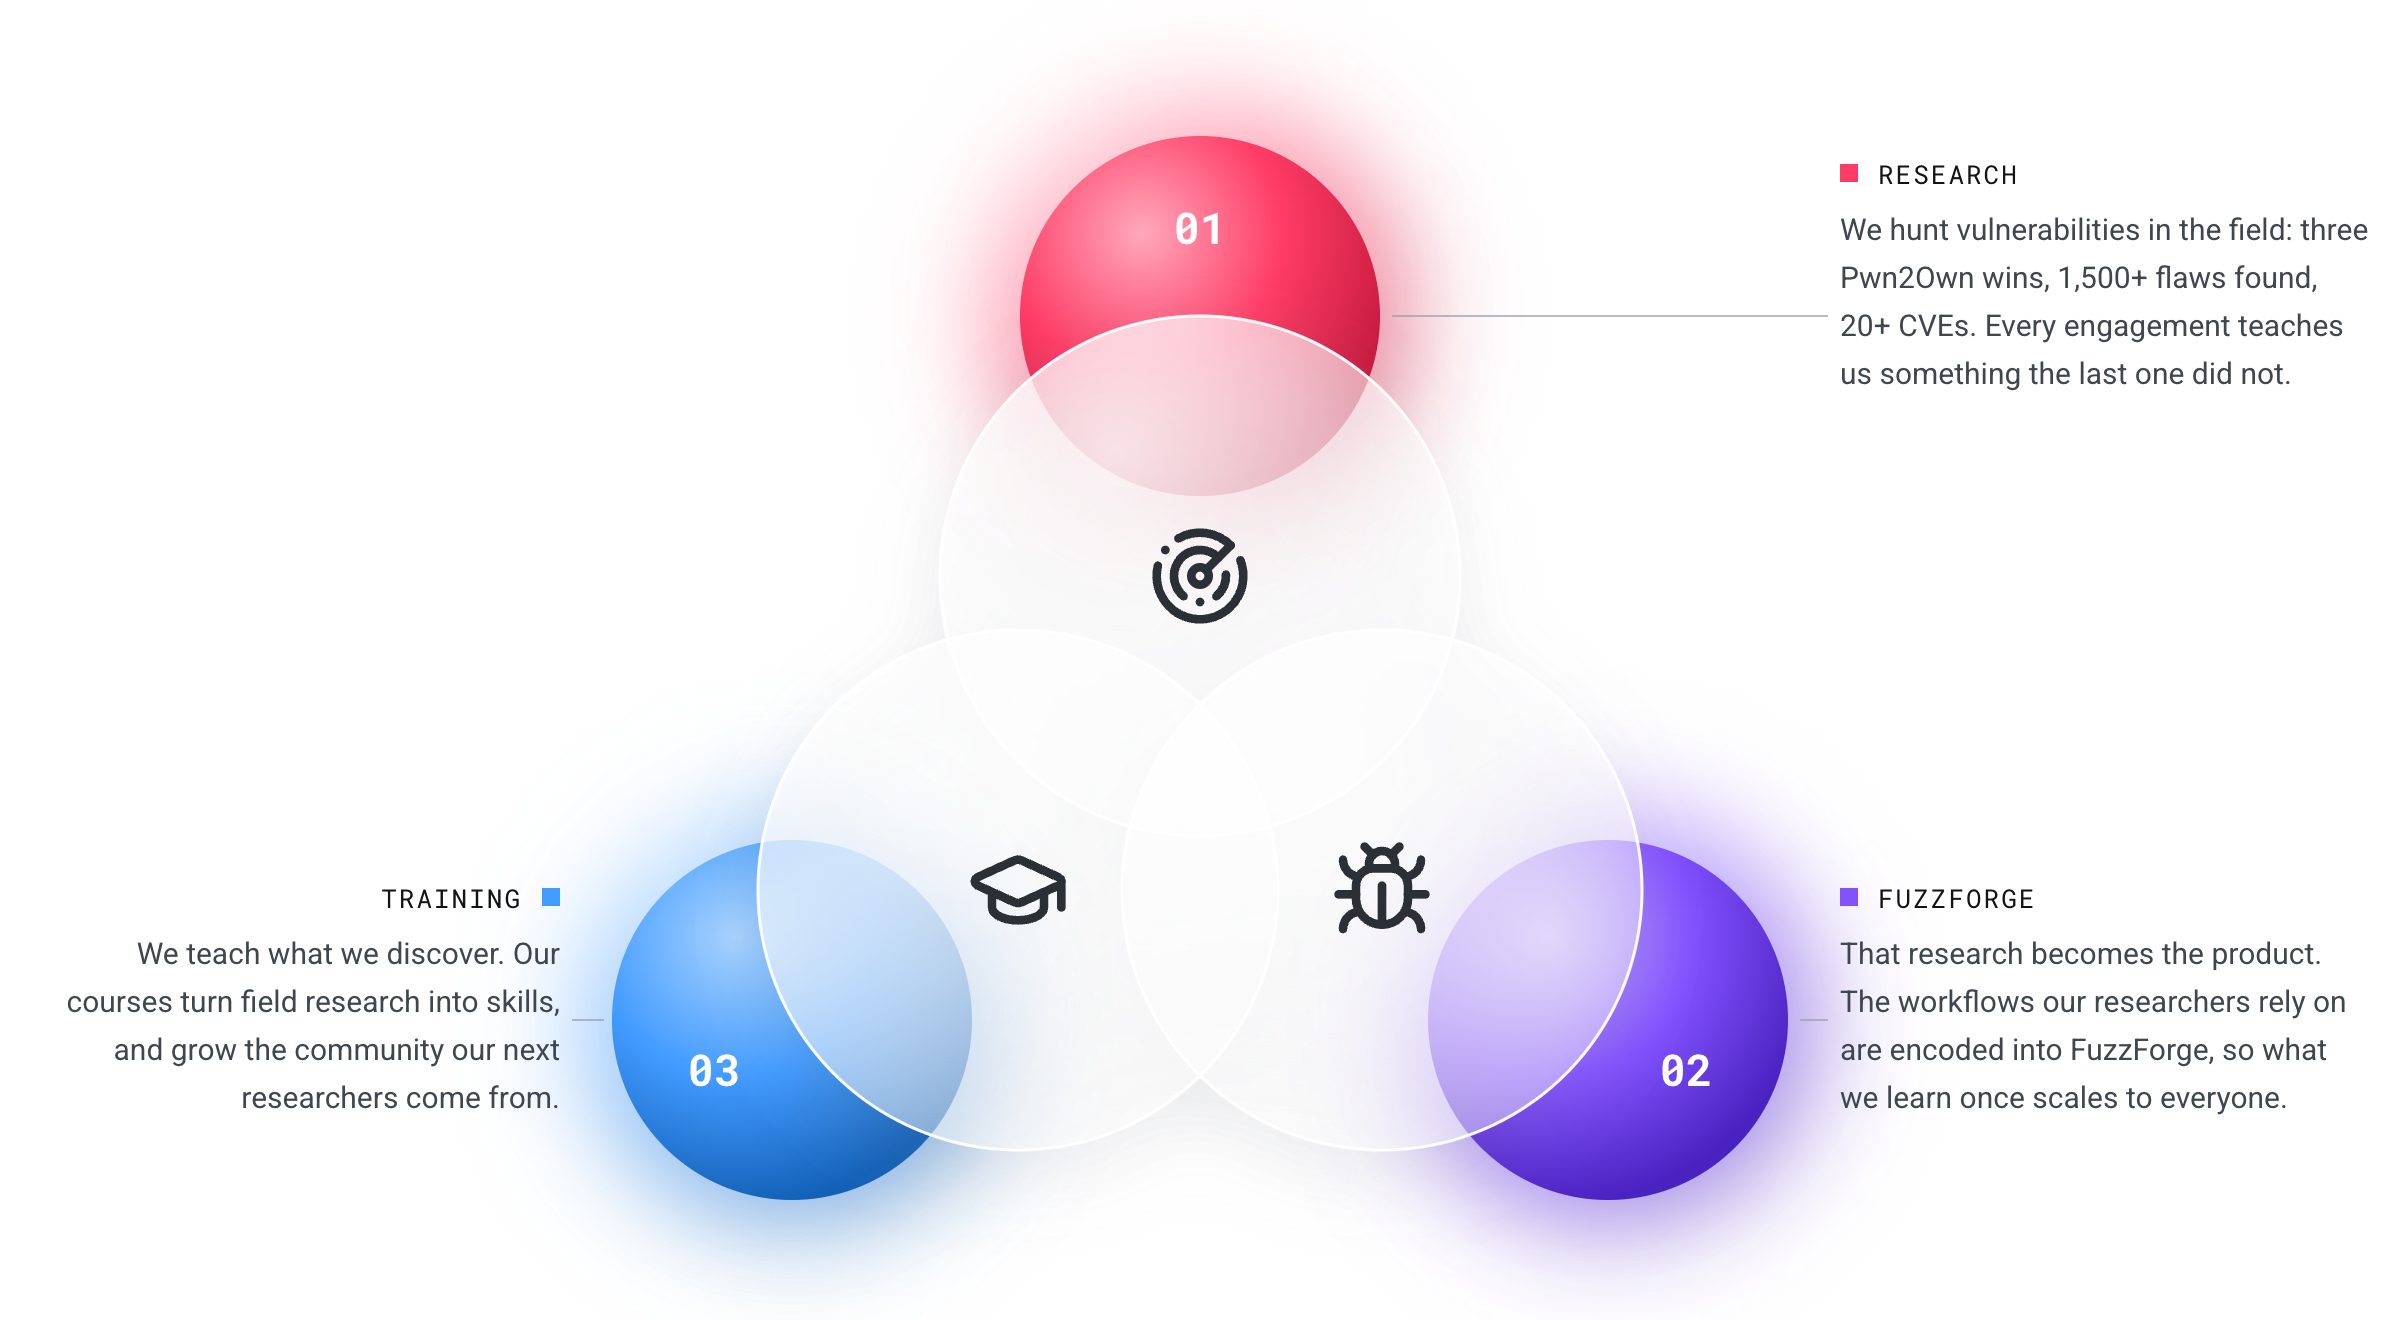
The more we research, the stronger FuzzForge and the training become. The more they grow, the more they feed the research.
INDUSTRIES WE SECURE

You ship a product built on binaries you do not fully own. Test it, and meet the CRA.

Validate the third-party code you approve, in a sovereign, on-prem environment.

Prove cyber-resilience under IACS UR E26 and E27, at build and at every annual survey.

Test the embedded software in your autonomous systems, without a large internal team.
Bring FuzzForge to your firmware and binaries, or train your team to find the bugs themselves.
| Cookie | Duration | Description |
|---|---|---|
| cookielawinfo-checkbox-analytics | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics". |
| cookielawinfo-checkbox-functional | 11 months | The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional". |
| cookielawinfo-checkbox-necessary | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary". |
| cookielawinfo-checkbox-others | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other. |
| cookielawinfo-checkbox-performance | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance". |
| viewed_cookie_policy | 11 months | The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data. |