

FOR MSSPS AND SECURITY INTEGRATORS
Test your clients’ firmware at every release, not once a year.
WHAT MAKES FIRMWARE SECURITY TESTING HARD FOR MSSPS
01
Firmware experts are rare.
→FuzzForge scales your offensive expertise.
Our engineers train your team on site to run it.
02
A pentest is out of date at the next release.
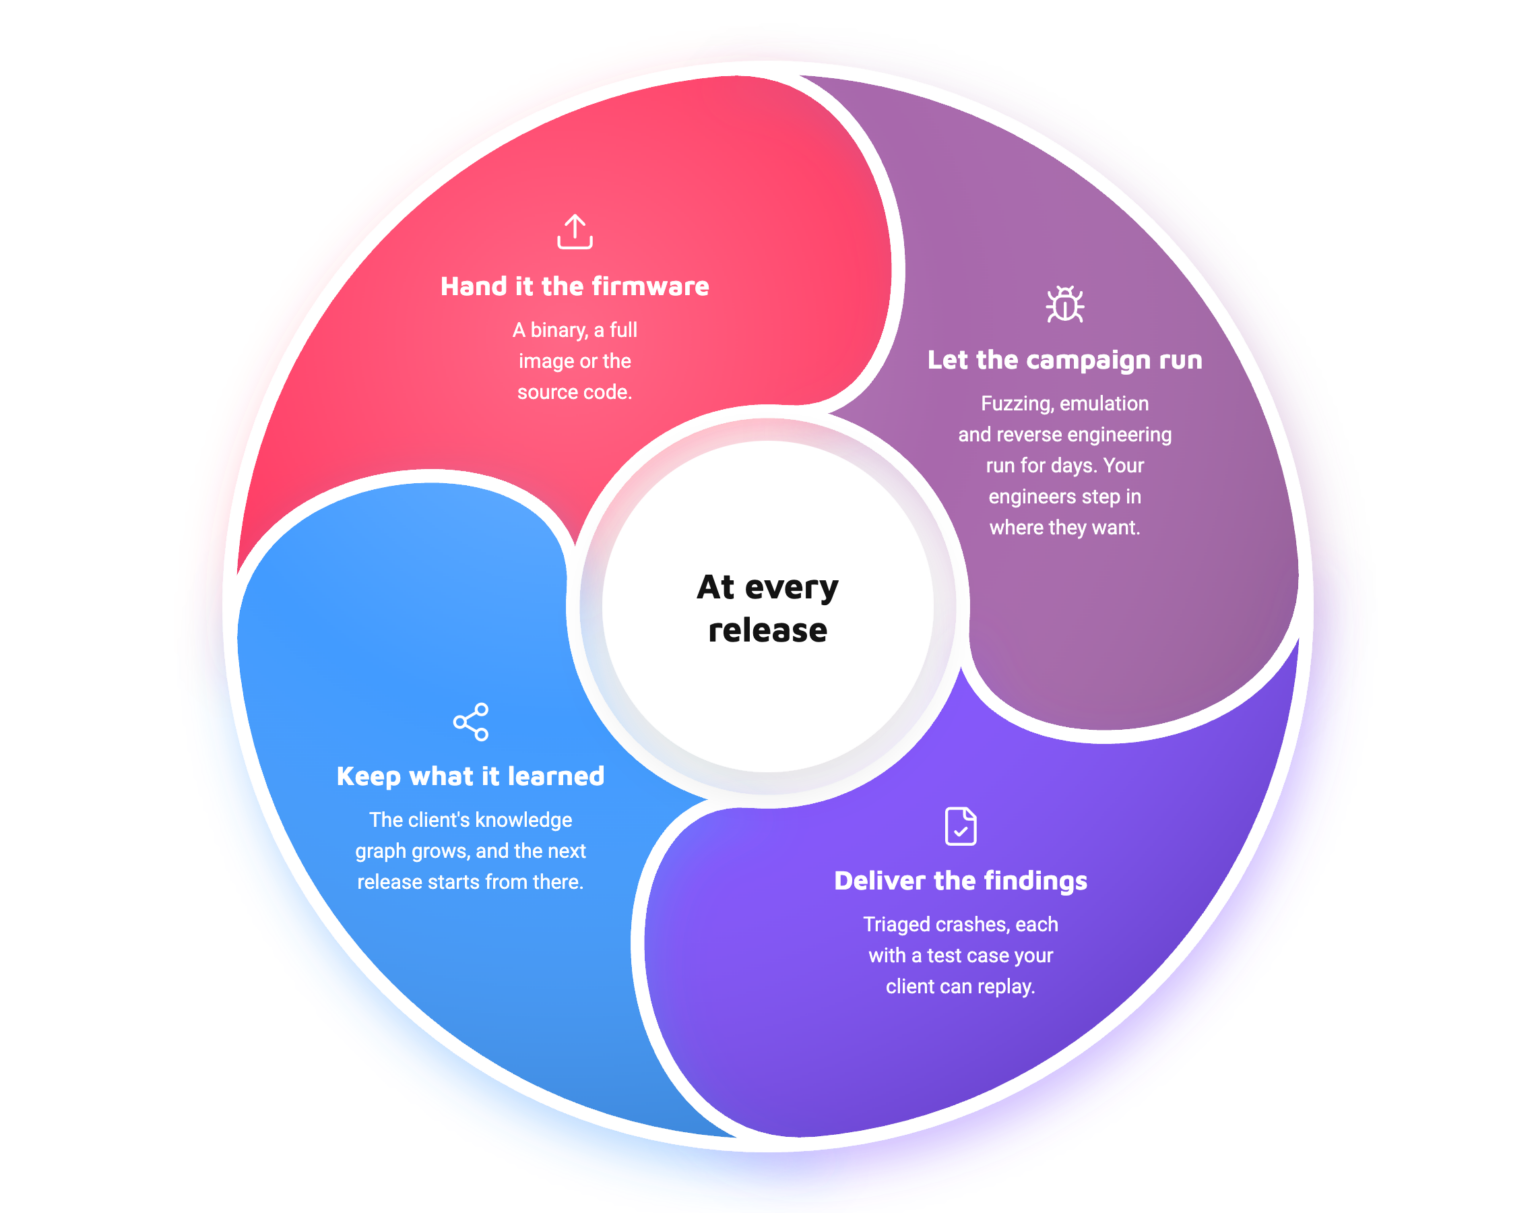
→Each campaign starts from the last one.
The knowledge graph keeps what every run learned.
03
Your clients’ firmware cannot leave their hands.
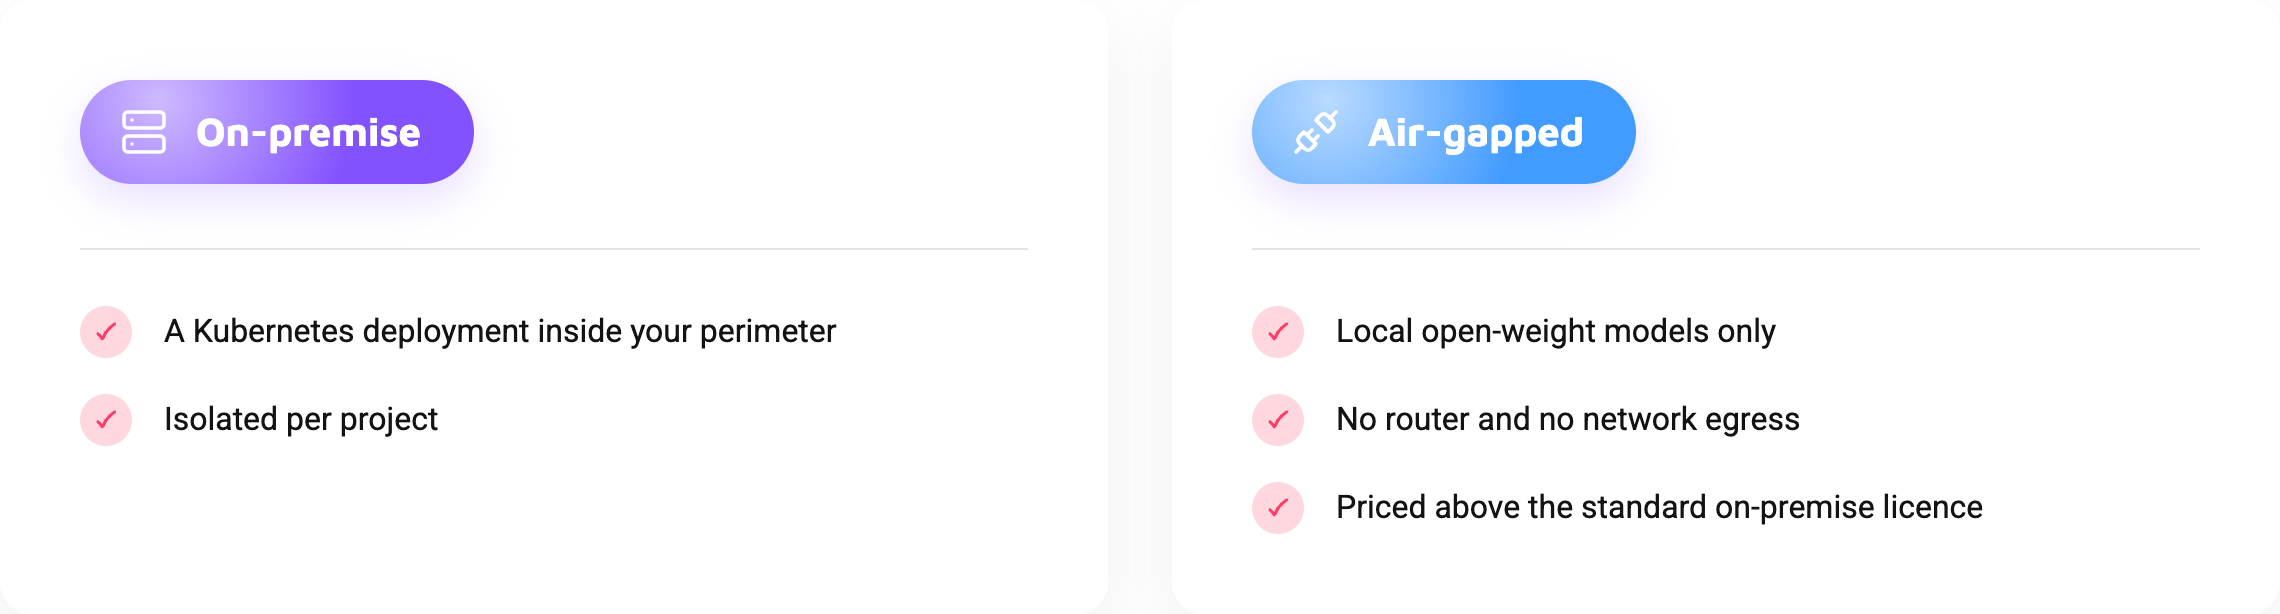
→FuzzForge runs on-premises.
Each client project stays isolated.
PROOF
WHERE IT RUNS
FAQ
Yes. You can run FuzzForge for your clients, or resell the licence to them. In both cases, FuzzingLabs keeps the platform itself.
A pentest covers one version, once or twice a year. FuzzForge runs a campaign at every release, replays findings after each fix, and keeps one knowledge graph per client.
No. FuzzForge runs the fuzzing, emulation and reverse engineering campaigns. Your engineers focus on the analysis, and ours train them on site to run the platform.
No. It works on compiled binaries, firmware images and source code. It writes the fuzzing harness itself.
On-premises, inside your perimeter or your client’s. An air-gapped option is available, priced above the standard on-premises licence.
A real campaign, on a target close to yours. Findings your engineers can pick up and verify.
MEET US
| Cookie | Duration | Description |
|---|---|---|
| cookielawinfo-checkbox-analytics | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics". |
| cookielawinfo-checkbox-functional | 11 months | The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional". |
| cookielawinfo-checkbox-necessary | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary". |
| cookielawinfo-checkbox-others | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other. |
| cookielawinfo-checkbox-performance | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance". |
| viewed_cookie_policy | 11 months | The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data. |