
New releases. New components. New security questions.
FuzzForge, the offensive validation platform built by FuzzingLabs, helps your team uncover and reproduce vulnerabilities through real execution. Keep security validation aligned with every release.
Selected and Trusted by





What has changed
New vulnerabilities and attack techniques emerge between assessments. Last year’s audit cannot tell you how today’s version holds up.
The EU Cyber Resilience Act puts vulnerability handling across the product lifecycle in focus. Your security evidence needs to keep pace with the products you maintain.
Investigating firmware and complex software takes specialist skills. Your release schedule won’t wait for your team to grow.
One audit a year can’t cover a product that keeps changing.
Make offensive validation continuous with FuzzingLabs.
Offensive research. Three ways to put it to work.
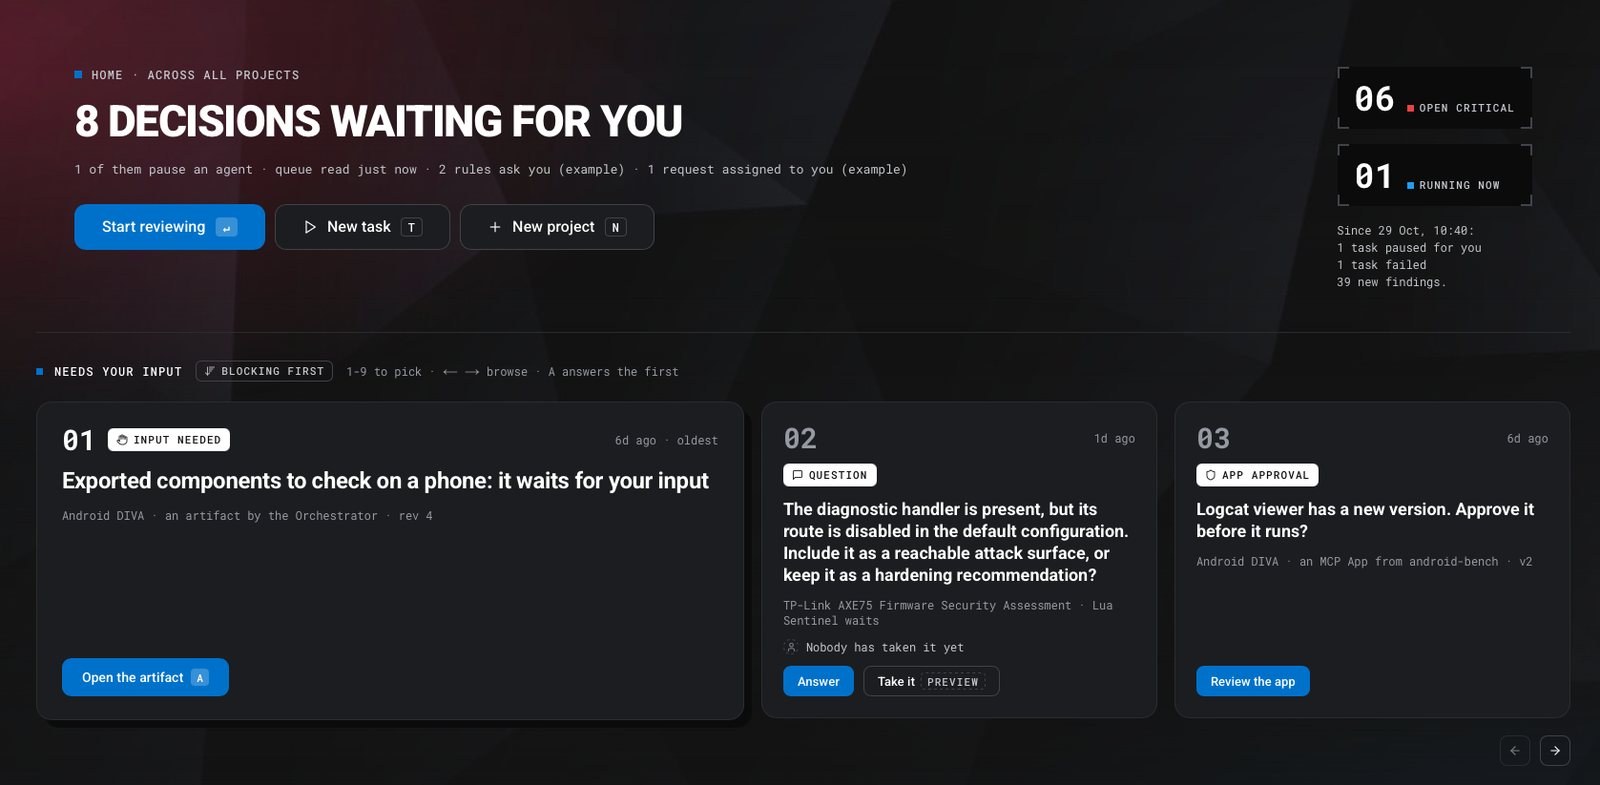
Offensive security platform
Bring repeatable offensive validation to your connected and embedded products. Investigate firmware, binaries and third-party components through real execution, with your experts directing the analysis.
Built by vulnerability researchers. Deployed on your premises.
Research
Put FuzzingLabs researchers to work on your toughest security questions. Get specialist support for advanced assessments and vulnerability research. Investigate hard-to-test software and understand what needs to be fixed.
Training
Build practical skills in fuzzing, reverse engineering and vulnerability research. Learn online at your own pace, or bring FuzzingLabs researchers directly to your engineering team.
What changes for your team
Give your team a head start on the next fix.
Find and investigate weaknesses before release. Give developers reproducible findings, then verify whether their corrections address the issue.
Have evidence ready when the questions come.
Document what was tested, what was found and what was validated. Support your vulnerability-handling processes and compliance work with evidence from real execution.
Your environment. Your models. Your control.
Run FuzzForge on your premises. Choose the AI models and deployment configuration that fit your operational and data requirements.
Who’s this for?
Your product. Your responsibility. Even when the code isn’t yours.
Assess the third-party firmware, compiled binaries and embedded components you ship, including those you cannot review at source-code level.
Sensitive software. Strict deployment requirements.
Investigate supplier code and critical components with a testing environment configured around your security constraints.
Your firmware evolves. Keep testing with it.
Assess embedded software and critical components as your product changes. Keep security validation aligned with the version you deploy.
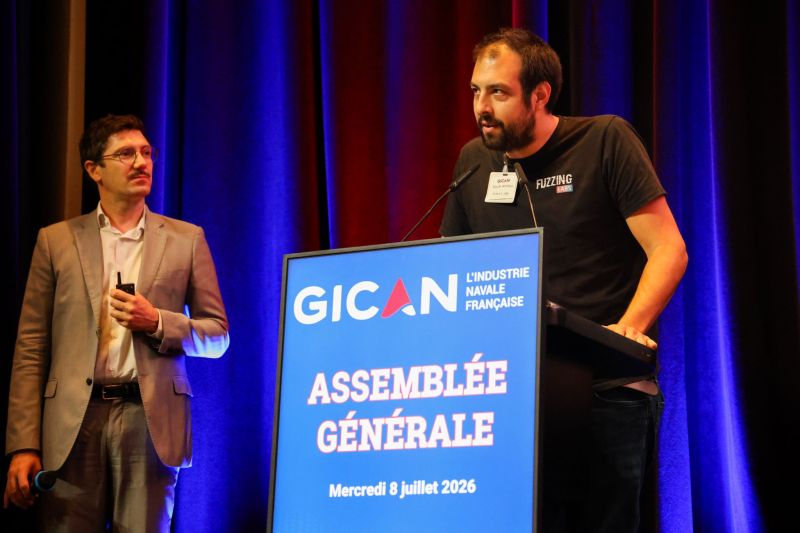
Patrick Ventuzelo at the GICAN general assembly, July 2026
Research is in our DNA
It started with one researcher.
Patrick Ventuzelo spent more than ten years hunting the flaws hidden in firmware and binaries. In 2021, he turned that passion into FuzzingLabs. And he started teaching it.
Today, FuzzingLabs is a French team of researchers and engineers. They compete at Pwn2Own, present at Black Hat and OffensiveCon, and pour that same drive into FuzzForge, the platform at the heart of the company.
FuzzingLabs brings that research-driven approach to FuzzForge, backed by recognition across the French security ecosystem:
Award
Laureate, Cyber Defense Factory (DGA)
Award
Finalist, Innovation Prize, Les Assises 2026
Award
Coup de Cœur, Nuit de la Sécurité Globale 2026
Programme
And a proud member of GICAN’s SEAstart programme
4
Pwn2Own wins
AI 2025 · IoT 2025 · Automotive 2026 · Ireland 2026
20+
CVEs published
6 on GNSS, AIS and NMEA
1,500+
Vulnerabilities found
In firmware, browsers, blockchains and open-source code
5,000+
Engineers trained
98% of students recommend our courses
Your next security challenge
Tell us what you’re building and where security testing gets difficult. Talk with a FuzzingLabs expert about the right next step: FuzzForge, a specialist assessment or training for your team.
Fresh from the lab
Explore published vulnerability research, sharpen your skills or catch the team at an upcoming event.
Events
16-18/11 · Rennes
Events
19-20/11 · Amsterdam
Research
15/10/2026
Training
| Cookie | Duration | Description |
|---|---|---|
| cookielawinfo-checkbox-analytics | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics". |
| cookielawinfo-checkbox-functional | 11 months | The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional". |
| cookielawinfo-checkbox-necessary | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary". |
| cookielawinfo-checkbox-others | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other. |
| cookielawinfo-checkbox-performance | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance". |
| viewed_cookie_policy | 11 months | The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data. |