PWN2OWN

Pwn2Own Ireland 2026: FuzzingLabs exploits the Brother MFC-L8970CDW with a single zero-day

At Pwn2Own Ireland 2026, two FuzzingLabs researchers, Lucas and Hugo, exploited the Brother MFC-L8970CDW business printer with a single zero-day. The entry earned $20,000 and 2 Master of Pwn points on October 8, the third day of the contest. The vulnerability has been reported to the Zero Day Initiative and Brother, and its details are confidential under coordinated disclosure.

EventPwn2Own Ireland 2026, Cork, October 6 to 9
TargetBrother MFC-L8970CDW (Printers category)
TeamLucas and Hugo, FuzzingLabs
ResultSuccess, with a single zero-day
Award$20,000 and 2 Master of Pwn points
StatusReported to ZDI and Brother through coordinated disclosure
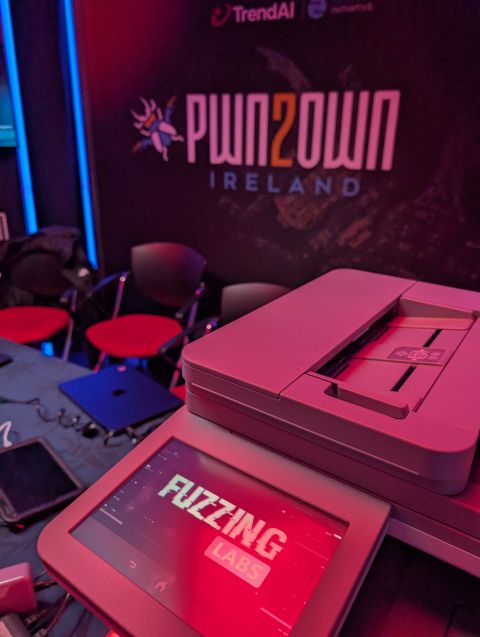
The Brother MFC-L8970CDW screen showing the FuzzingLabs logo at Pwn2Own Ireland 2026

What happened at Pwn2Own Ireland 2026?

Lucas and Hugo took the Brother MFC-L8970CDW on day three. One bug was enough to take control of the printer. ZDI confirmed the result in its day three report.

The printer had already been targeted twice that week. Both earlier attempts were unsuccessful, on day one and on day two.

What is Pwn2Own?

Pwn2Own is a hacking competition run by the Zero Day Initiative (ZDI). Researchers exploit widely used devices and software live, within a fixed time slot. Every working exploit is bought by ZDI and reported to the vendor.

A few things to know:

  • It started in April 2007, at the CanSecWest conference in Vancouver.
  • It now runs three times a year. Recent editions have each paid out more than $1 million.
  • A random draw sets the order of attempts. The first team to succeed on a target earns the full prize.
  • Every success earns points. The researcher or team with the most points wins the “Master of Pwn” title.

The 2026 Ireland edition took place in Cork from October 6 to 9, with more than 60 entries. The rules list seven categories: mobile phones, smart home, wellness, printers, messaging, AI infrastructure and coding agents. The printer category had three targets from Brother, Lexmark and Canon, each worth $20,000 and 2 Master of Pwn points. Ikotas Labs won the Master of Pwn title.

Why are printers a target?

An office printer is a networked computer that few people think of as one. It sits on the corporate network, processes untrusted input and runs complex embedded firmware. That is exactly the attack surface our team works on every day, from embedded systems to network-facing devices.

The MFC-L8970CDW is a good example. Brother sells it as a business color laser all-in-one that prints, copies, scans and faxes. It connects over Gigabit Ethernet and dual-band Wi-Fi, and it integrates with Active Directory. Each of those features is code that parses data coming from the network.

Brother printers have been here before. In June 2025, Rapid7 disclosed eight vulnerabilities affecting 748 printer, scanner and label maker models across five vendors, 689 of them from Brother. The most severe, CVE-2024-51978 (CVSS 9.8), let a remote attacker derive the default administrator password from the device serial number. Brother stated it could not be fully fixed in firmware. Japan’s JPCERT/CC published the official advisory.

The rest of the printer category confirms the pattern. At Ireland 2026, the Lexmark and Canon targets were also exploited by several teams.

What happens to the vulnerability now?

It goes through coordinated disclosure. The technical details are currently confidential.

Under ZDI’s disclosure policy:

  • ZDI reports the vulnerability to the vendor.
  • The vendor gets 120 days to release a fix.
  • If no fix arrives in time, ZDI publishes a limited advisory with mitigations.

Until then, owners of networked printers can apply the basics. Install firmware updates as soon as they are released. Change the default administrator password. Keep the management interface off networks that do not need it.

What does this say about firmware security?

Breaking a printer takes the same skills as testing any embedded product. You need to understand the firmware, find where it trusts its input, and prove that a bug can actually be exploited.

That is the work our team does every day. FuzzingLabs researchers have won at Pwn2Own in the AI, IoT and automotive categories, and our research has uncovered more than 1,500 vulnerabilities and 20+ CVEs (see our trophies). Recent work includes spoofing RTKLIB, the library behind centimeter-accurate GPS, and hunting bugs in the batman-adv mesh protocol.

That know-how also goes into FuzzForge, an autonomous offensive security platform for firmware, binaries and embedded systems. It runs fuzzing, emulation and reverse engineering campaigns at scale. If you build connected products, see how we work with embedded product vendors and OEMs.

FAQ

It is the fall edition of Pwn2Own, a hacking competition run by the Zero Day Initiative. It was held in Cork, Ireland, from October 6 to 9, 2026, with more than 60 entries across categories such as printers, mobile phones and smart home devices.

The Brother MFC-L8970CDW, a business color laser all-in-one. Lucas and Hugo exploited it with a single zero-day on October 8, earning $20,000 and 2 Master of Pwn points.

Not yet. It was reported to ZDI and Brother through coordinated disclosure, and its technical details are currently confidential.

A vulnerability that the vendor does not know about yet, so no fix exists when it is found.

The title given to the researcher or team with the most points across a Pwn2Own edition. Every successful exploit earns points.

Patrick Ventuzelo, CEO & Founder of FuzzingLabs·LinkedIn

About Us

FuzzingLabs was founded in 2021 by Patrick Ventuzelo, a vulnerability researcher who spent more than ten years finding the flaws hidden in firmware and binaries. He built FuzzingLabs to turn that passion into a company, and to teach it.

Today, FuzzingLabs is a French team of researchers and engineers. They compete at Pwn2Own, present at Black Hat and OffensiveCon, and pour that same passion into FuzzForge, the platform at the heart of the company.

Keep in touch with us !

email

contact@fuzzinglabs.com

X

@FuzzingLabs

Github

FuzzingLabs

LinkedIn

FuzzingLabs

email

contact@fuzzinglabs.com

X

@FuzzingLabs

Github

FuzzingLabs

LinkedIn

FuzzingLabs