FOR PRODUCT SECURITY TEAMS AND PSIRTs
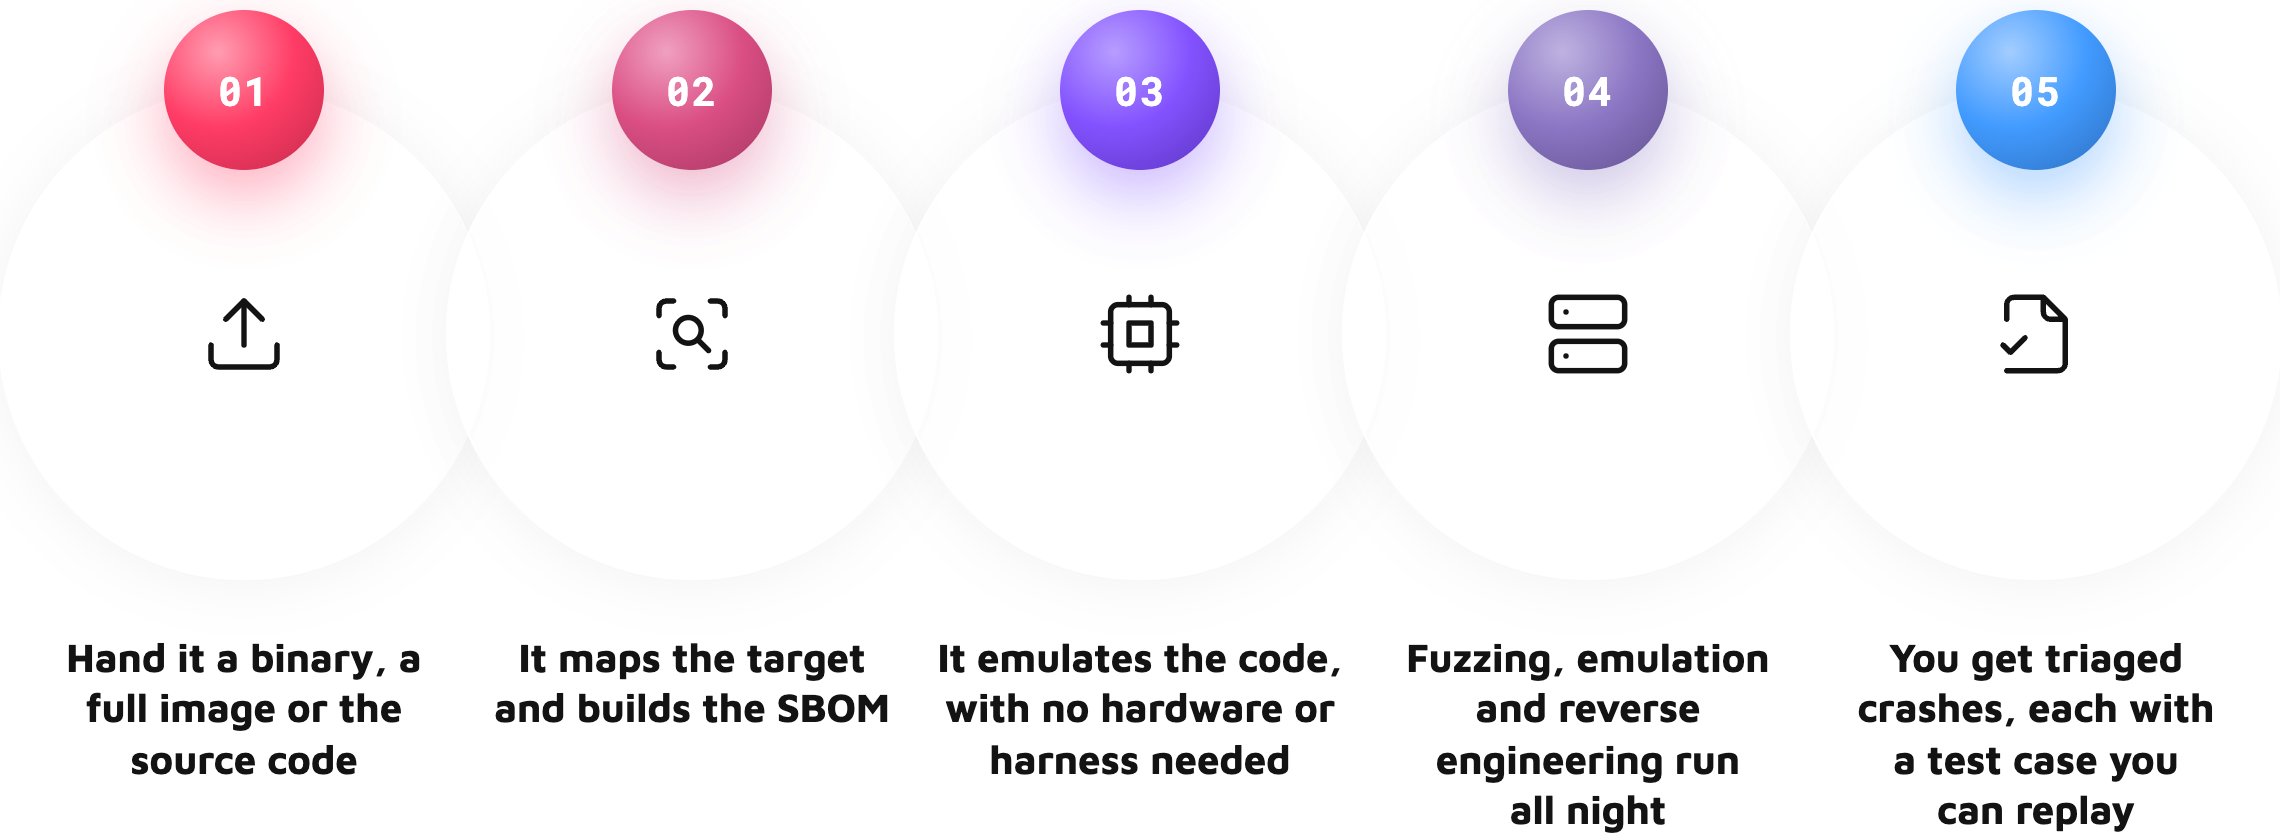
FuzzForge runs the fuzzing, emulation and reverse engineering campaigns your team never has the capacity to launch.
THE PROBLEM
Nobody has ever audited your drivers or your protocol parsing.
On a packed firmware or a stripped binary, you have neither.
They run for days, and product releases come first.
HOW IT WORKS
ARCHITECTURE
Scheduled on available compute, so long campaigns actually finish.
They use the industry tools your team already knows.
So the sixth month is worth more than the first.
Every model request and reasoning chain is logged.
PROOF
DEPLOYMENT
WHO IT IS FOR
FAQ
No. FuzzForge works on binaries and firmware images. It writes the fuzzing harness itself, which is usually the part that requires the source.
Neither. It is an offensive infrastructure that runs fuzzing, emulation and reverse engineering, with agents driving the campaigns.
Firmware images and stripped binaries, including third-party components you ship without their sources.
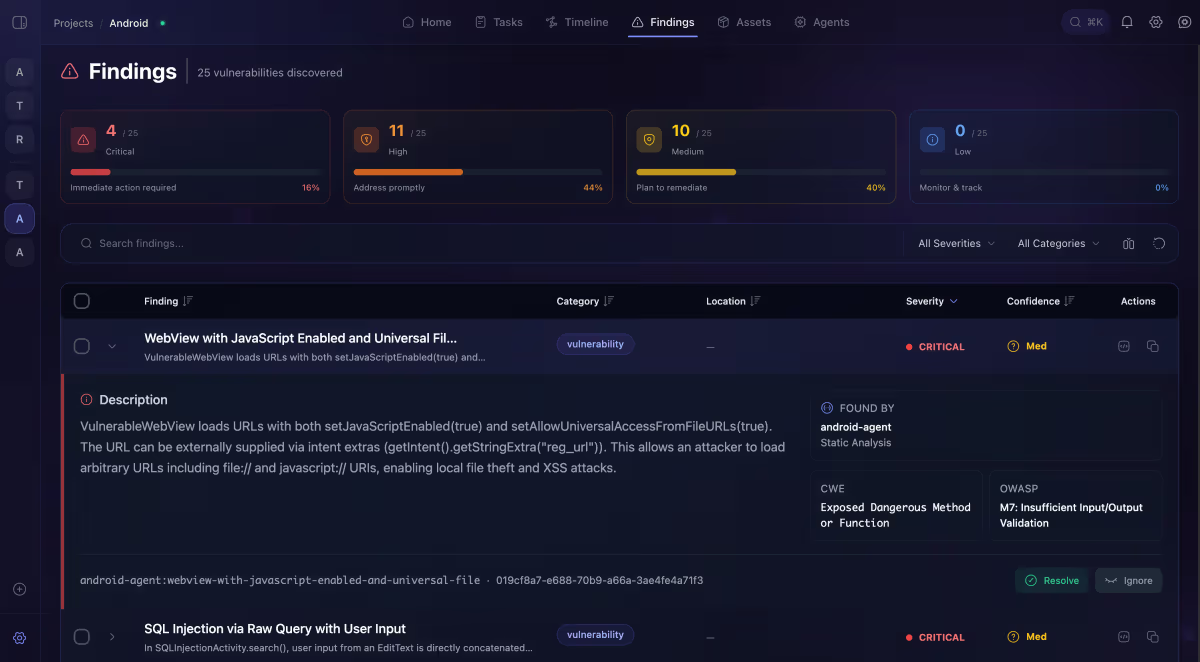
A validated finding with a test case your developers can replay, and crashes already deduplicated and triaged. You also get an SBOM built from the binary itself. You keep the test cases, the reports, the configurations and your own knowledge graph. FuzzingLabs keeps the platform itself.
It does not replace your researchers, and it is not a source-code scanner. It runs on the compiled artifact, on the code nobody has audited, and it takes the campaigns your team has no time for. A useful campaign runs for days, not minutes.
A real campaign, on a target close to yours. Findings your engineers can pick up and verify.
MEET US
| Cookie | Duration | Description |
|---|---|---|
| cookielawinfo-checkbox-analytics | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics". |
| cookielawinfo-checkbox-functional | 11 months | The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional". |
| cookielawinfo-checkbox-necessary | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary". |
| cookielawinfo-checkbox-others | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other. |
| cookielawinfo-checkbox-performance | 11 months | This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance". |
| viewed_cookie_policy | 11 months | The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data. |