REcon 2025 - Training Announcement
Rust Development for Cybersecurity Training
Dive into the world of cutting-edge cybersecurity tools with our exclusive Rust Development for Cybersecurity Training! Led by experts Matthieu Christophe and Tanguy Duhamel, this hands-on program will equip you with advanced Rust techniques to build defensive and offensive security tools, unlocking your potential to master memory safety, networking, OSINT, forensics, and even offensive frameworks.
Overview
Rust is revolutionizing cybersecurity development by combining performance with memory safety, making it the ideal language for building secure and efficient tools. This hands-on training is designed for professionals looking to harness the power of Rust to develop cutting-edge security solutions for both defensive and offensive purposes.
The training begins with a solid foundation in Rust’s fundamentals, covering key concepts like ownership, borrowing, and concurrency to ensure participants are fluent in Rust’s unique features. From there, attendees will delve into practical applications, including building CLI tools, networking utilities, and modular security tools. Advanced topics like memory forensics, OSINT automation, and in-memory vulnerability analysis are also covered, each designed to simulate real-world scenarios.
Participants will explore high-performance techniques like multithreaded port scanning, implementing secure C2 frameworks, and integrating memory scanning with network packet monitoring. By the end of the course, attendees will not only have mastered Rust basics but will also possess the skills to build sophisticated tools for threat detection, analysis, and offensive security operations.
23rd-26th of June 2025
ReCon (Montreal, Canada)
4 days
Intermediate
Matthieu Christophe & Tanguy Duhamel
$5500 (before May 1st) - $6000
25 participants
Schedule
Day 1
- Morning: Foundations of Rust for Cybersecurity Tools
- Afternoon: Advanced Rust Techniques for Modular Security Tools
Day 2
- Morning: High-Speed OSINT with Rust
- Afternoon: In-Memory Forensics and Process Analysis
Day 3
- Morning: Rapid Recon and Vulnerability Mapping
- Afternoon: Fuzzing Building a Command and Control (C2) Framework
Day 4
- Morning: Network Traffic Monitoring and Threat Detection
- Afternoon: Advanced Forensics and Memory Integration
Your Instructors
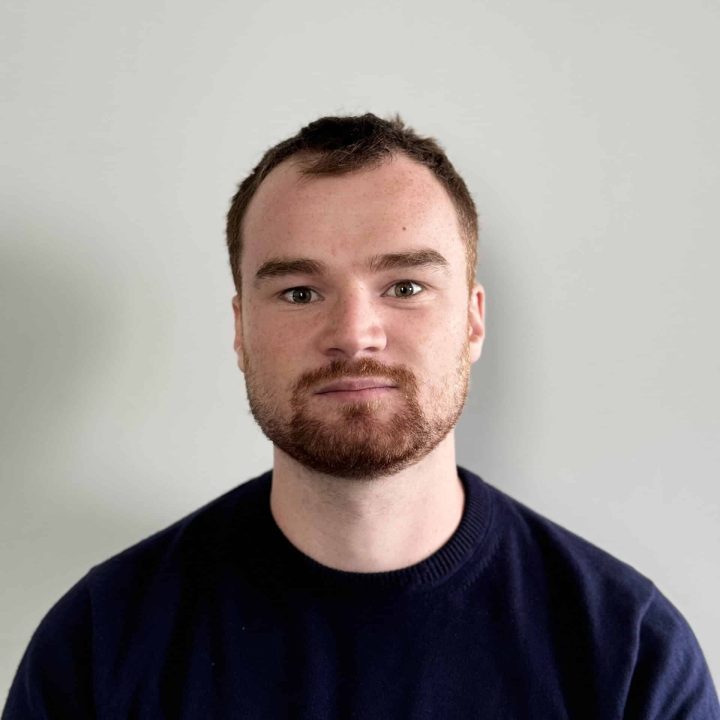
Tanguy Duhamel
Tanguy Duhamel is the Lead Developer on FuzzingLabs' distributed fuzzing platform, collaborating with Patrick Ventuzelo on code auditing, fuzzer development, and security research. His research focuses on advancing distributed fuzzing techniques to improve software security, with a strong foundation in Rust for building high-performance tools.
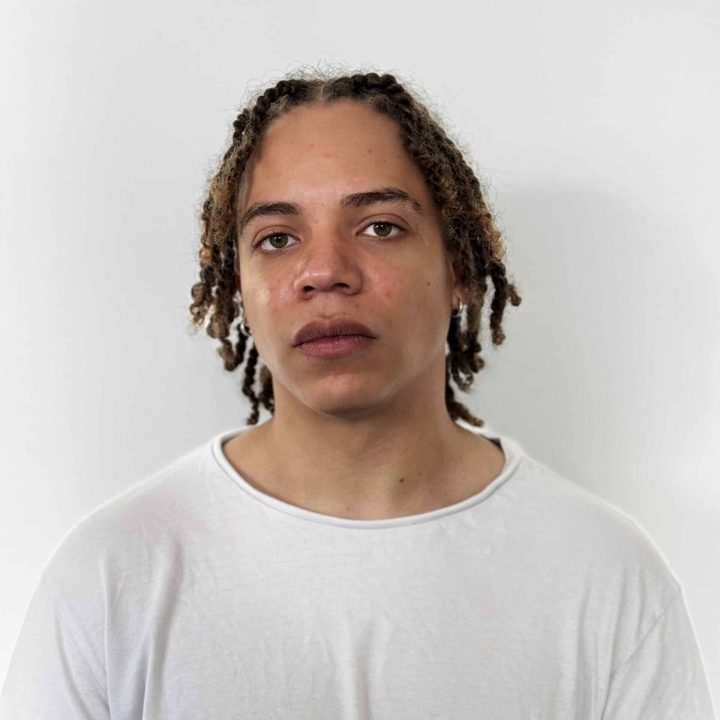
Matthieu Christophe
Christophe Matthieu is a security engineer who studied Computer Science and Offensive Security, with experience in major companies across critical sectors such as energy, banking, and automotive. Now part of FuzzingLabs, he works as a security researcher specializing in hardware and network security.
Topics Covered
Day 1: Introduction and Fundamentals
- Morning: Foundations of Rust for Cybersecurity Tools
- Ownership, borrowing, and memory safety
- Concurrency and multithreading basics
- Error handling in Rust
- Building CLI tools and managing configurations
- Networking basics with Rust
- Afternoon: Advanced Rust Techniques for Modular Security Tools
- Lifetimes and advanced ownership patterns
- Smart pointers (
Rc,Arc,Mutex) and interior mutability - Designing modular and extensible Rust applications
- Handling file system events
Day 2: Defensive Security Tools
- Morning: High-Speed OSINT with Rust
- Web scraping and crawling with async Rust
- Interacting with APIs and JSON for OSINT
- Extracting useful metadata and subdomain enumeration
- Afternoon: In-Memory Forensics and Process Analysis
- Understanding memory process structures
- Using Rust for memory scanning and dumping
- Analyzing dumped data for patterns or sensitive information
Day 3: Offensive Security
- Morning: Rapid Recon and Vulnerability Mapping
- Writing high-performance port scanners in Rust
- Using async Rust for parallel scanning
- Automating basic vulnerability detection
- Afternoon: Building a Command and Control (C2) Framework
- Basics of RAT (Remote Access Tool) development
- Securely managing communication between client and server
- Cross-platform considerations for offensive tools
Day 4: Hands-On Project – Building an Antivirus & EDR
- Morning: Network Traffic Monitoring and Threat Detection
- Capturing network packets with Rust libraries (
pcap,libpnet) - Parsing and filtering network traffic for actionable insights
- Detecting malicious payloads (e.g., URLs, patterns)
- Capturing network packets with Rust libraries (
- Afternoon: Advanced Forensics and Memory Integration
- Integrating forensic tools into an EDR framework
- Refining memory scanning and analysis techniques
- Correlating memory dumps with network monitoring insights
Prerequisites and requirements
- Familiarity with Linux and Rust.
- A working laptop capable of running virtual machines
- 4GB RAM required, at a minimum
- 40 GB free Hard disk space
- VirtualBox
- Administrator/root access MANDATORY
This course is suitable for people that are new to Rust. All the theory and concepts about Rust security and Rust fuzz testing will be explained during the course.
About Us
Founded in 2021 and headquartered in Paris, FuzzingLabs is a cybersecurity startup specializing in vulnerability research, fuzzing, and blockchain security. We combine cutting-edge research with hands-on expertise to secure some of the most critical components in the blockchain ecosystem.
Any questions about our services and trainings ?
Let’s work together to ensure your peace of mind.
LATEST ARTICLES